TerraformDevSecOpsPolicy as CodeAWSGitHub Actions
Automated Terraform Security & CIS Compliance Guardrails
Policy-as-code validation pipeline testing Terraform plans against CIS AWS Foundations Benchmark using Checkov and GitHub Actions.
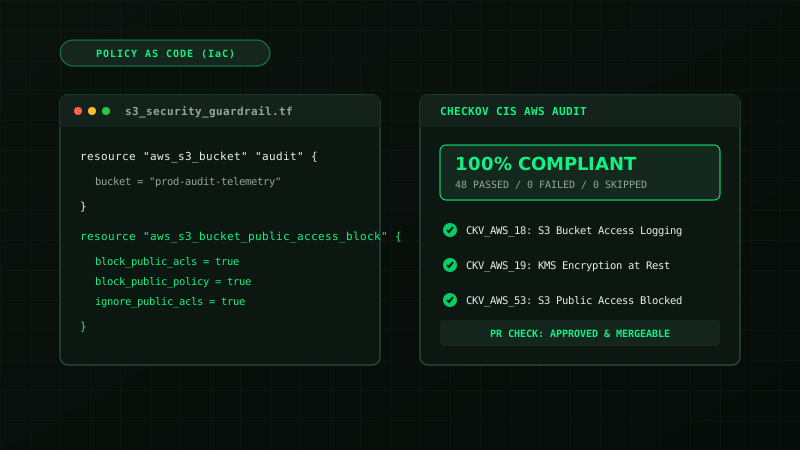
A automated DevSecOps validation framework designed to prevent misconfigured cloud infrastructure from ever being provisioned. Integrated into GitHub Actions pull request checks, the pipeline parses Terraform HCL code and compiled plan JSONs.
Implementation Workflow
- Pre-commit Hooks: Developer workstations run
tflintandterraform fmtlocally before pushing code. - Static Code Analysis: Checkov scans all
.tffiles against over 300 built-in security policies. - Plan Evaluation: Terraform outputs a binary plan file, converted to JSON, and tested against custom Open Policy Agent (OPA) / Conftest rules.
name: Terraform Security Gate
on: [pull_request]

jobs:
  scan-terraform:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v4
      - name: Run Checkov Static Analysis
        uses: bridgecrewio/checkov-action@master
        with:
          framework: terraform
          output_format: cli
          soft_fail: false