AWSAuth0DockerPythonFHIRZero-Trust
AWS Zero-Trust Healthcare Microservices & Auth0 IAM
HIPAA-oriented cloud architecture implementing Auth0 fine-grained RBAC, private API gateway endpoints, and automated audit trails for healthcare workloads.
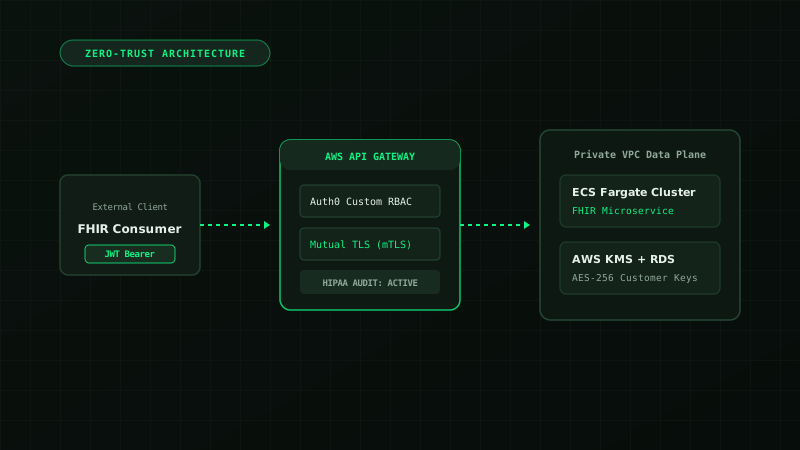
An enterprise cloud deployment engineered to satisfy strict HIPAA and SOC 2 Type II compliance constraints. The system isolates sensitive Electronic Health Record (EHR) data behind private VPC endpoints while federating authentication through Auth0.
Architecture Topology
    flowchart TD
  Client[Web & Mobile Clients]
  Auth0[Auth0 Identity Platform]

  subgraph AWS ["AWS Cloud (VPC Isolated)"]
      APIGW[API Gateway (Private VPC Link)]
      subgraph Compute ["ECS Fargate Cluster"]
          AuthService[Auth Verification Service]
          FHIRProxy[FHIR Proxy Service]
      end
      subgraph Storage ["Encrypted Data Plane"]
          Aidbox[(FHIR / Aidbox Store)]
          KMS[AWS KMS Customer Managed Keys]
      end
  end

  Client -->|1. Authenticate with MFA| Auth0
  Auth0 -->|2. Issue Scoped JWT| Client
  Client -->|3. HTTPS Request with Bearer Token| APIGW
  APIGW --> AuthService
  AuthService -->|4. Validate Claims & Permissions| FHIRProxy
  FHIRProxy -->|5. TLS mTLS Encrypted Query| Aidbox
  Aidbox -.-> KMS
Technical Highlights
- Role-Based Access Control (RBAC): Auth0 Custom Actions validating user organizational membership and assigning patient-level scopes (
patient/*.read). - Encrypted Storage: PostgreSQL RDS database with KMS customer-managed key encryption and automatic rotation.
- Audit Logging: Structured JSON logging streaming into AWS CloudWatch with automated alerting for unauthorized access attempts (
403 Forbidden).