Distributed HoneyNet & Automated Threat Intelligence
Multi-region decoy sensor array trapping automated exploitation attempts, analyzing malware payloads, and publishing live threat feeds to SIEM.
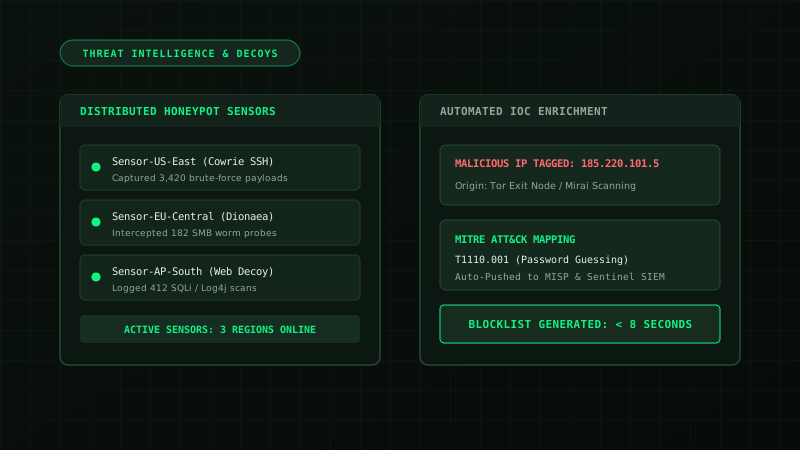
Production-grade cloud security architectures, automated CI/CD guardrails, threat intelligence pipelines, and eBPF runtime probes.
Multi-region decoy sensor array trapping automated exploitation attempts, analyzing malware payloads, and publishing live threat feeds to SIEM.
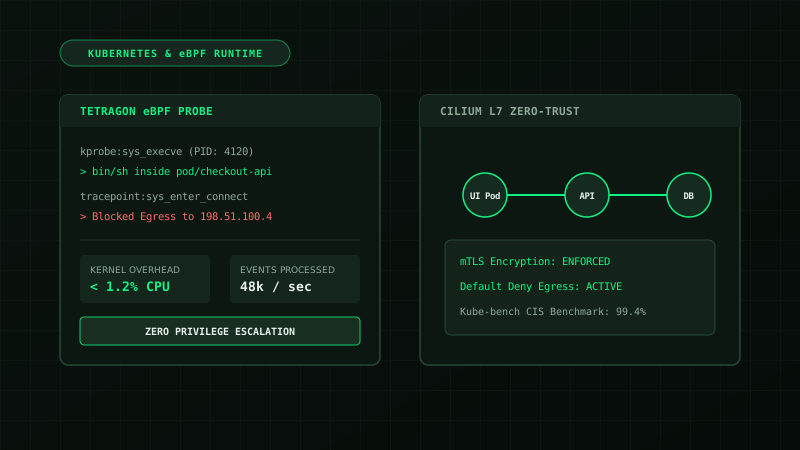
Production Kubernetes cluster hardening using Cilium network policies, Tetragon eBPF kernel event tracing, and Falco runtime alerting.
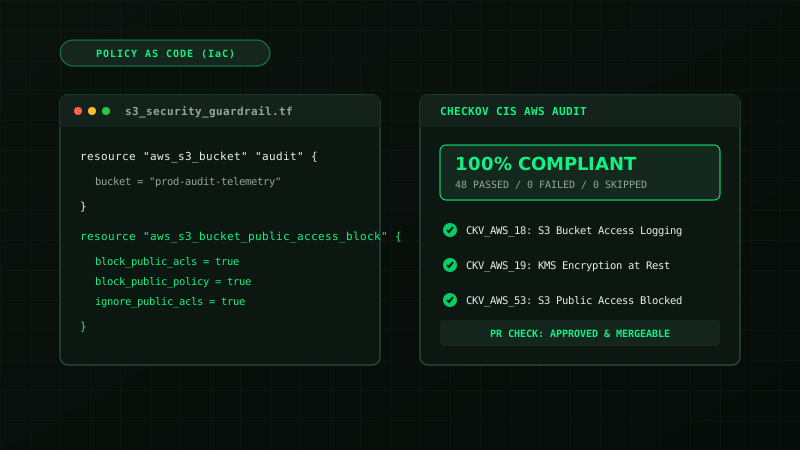
Policy-as-code validation pipeline testing Terraform plans against CIS AWS Foundations Benchmark using Checkov and GitHub Actions.
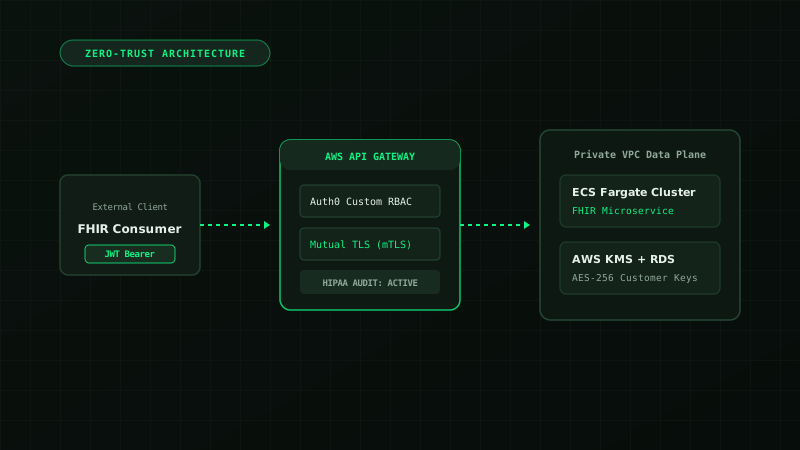
HIPAA-oriented cloud architecture implementing Auth0 fine-grained RBAC, private API gateway endpoints, and automated audit trails for healthcare workloads.
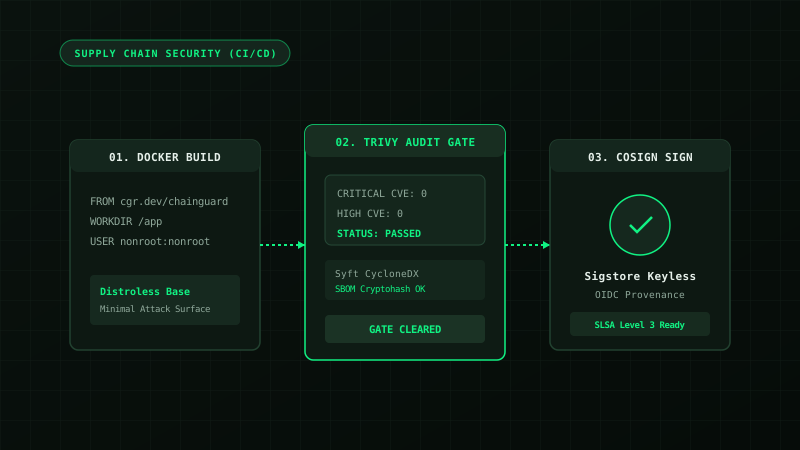
CI/CD DevSecOps pipeline using GitHub Actions, Trivy, and Cosign to verify cryptographic container signatures and block vulnerable images.
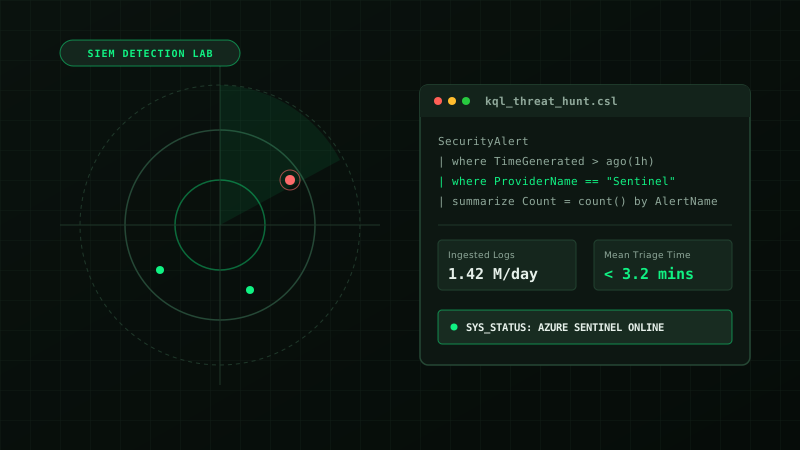
Full-cycle Azure cloud defense lab simulating multi-tier network isolation, Microsoft Sentinel log ingestion, and automated threat hunting rules.